
 By
Your laptop feels slow and you suspect hidden malware, but you don't know how much RAM a virus actually consumes. This page tells you the typical memory footprint of common threats and shows you exactly where to look in Task Manager to spot the culprit.
In short: Most standard malware uses 20–100 MB of RAM, but aggressive crypto-miners or rootkits can spike usage to 500 MB or more. If you see an unknown process using over 200 MB without a clear purpose, it is likely malicious. The best way to verify is to sort Task Manager by memory usage and check the file location of any suspicious entries.
Our pick
Tap to see today's price on Amazon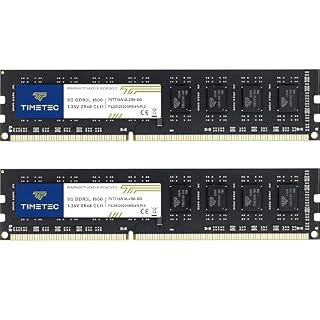
Adding more RAM prevents the system from swapping to disk, which makes it easier to spot genuine malware spikes.
How much memory does malware usually consume?
There is no single fixed number because malware varies wildly by type. Simple adware or trojans often run quietly in the background, using as little as 15–50 MB of RAM. This low footprint helps them hide from casual checks. If that sounds like your bench, read up on monitoring your internal heat levels next.
More sophisticated threats, like crypto-miners or fileless viruses, are much heavier. A miner working to decrypt coins can easily consume 300–1,000 MB while running. This sustained high usage is what often drives a PC to feel sluggish.
- Adware/Browser Hijackers: 20–100 MB (often tied to a browser process).
- Ransomware/Stagers: 50–200 MB (short bursts during encryption).
- Crypto-Miners: 400–1,000+ MB (continuous high usage).
Keep in mind that legitimate heavy applications also use this much. A game or video editor can use 1GB+. The red flag is high memory usage from a process you do not recognize or did not start.
Pro tip: Do not assume high memory usage is always malware. Always check the 'CPU' column too; malware often runs at 100% CPU along with high RAM.
What normal baseline memory looks like on your PC
Before you judge a spike, you need to know your system’s normal state. A fresh boot of Windows 11 typically uses 4–6 GB of RAM total, including all background services. macOS Sonoma usually sits between 5–8 GB depending on background apps.
If your laptop has 8 GB of RAM, it is likely running near capacity just to handle the OS. In this scenario, even a small malware load can push the system into ‘swap’ mode, where it uses the hard drive as virtual memory. This makes the PC feel frozen.
If you have 16 GB, you have headroom. A malware spike of 500 MB is noticeable but won’t crash the system immediately. This headroom is why high-end systems often mask infection symptoms until it is too late. Before you buy anything, it is worth looking at spotting malicious code in activity monitors.
Upgrading to 16GB gives you enough headroom to distinguish a malware spike from normal OS overhead.
- PCB color may vary (black or green) depending on production batch. Quality and
- DDR3L / DDR3 1600MHz PC3L-12800 / PC3-12800 240-Pin Unbuffered Non-ECC 1.35V / 1.5V
How to spot a malware spike in Task Manager
Press Ctrl + Shift + Esc to open Task Manager directly. Go to the ‘Processes’ tab. Look for the ‘Memory’ column. You are not looking for the highest user, but for the most suspicious one.
Click the column header ‘Memory’ to sort from highest to lowest. Ignore your web browser if it has many tabs open. Look below the top 5 entries. You are hunting for a process with a weird name (e.g., svchost32.exe instead of svchost.exe) or a generic name like WinUpdate or SystemProcess that is not on the Microsoft list.
Right-click the suspicious process. Select ‘Properties’. Note the file path. Legitimate Windows files live in C:Windows or C:Program Files. If a high-memory process is running from C:UsersYourNameDownloads or C:Temp, it is almost certainly malware.
Common myths about malware memory usage
Myth: Malware always runs at 100% CPU.
Fact: Many pieces of malware are designed to be stealthy. They run in short bursts to download commands or log keystrokes, keeping resource usage low to avoid detection.
Myth: My antivirus says I’m clean, so memory is safe.
Fact: Antivirus signatures update daily. New, zero-day malware may not be in the signature database yet. Behavioral analysis in Task Manager is a manual safety net.
Myth: High memory usage means I need more RAM.
Fact: Sometimes it just means a runaway process or a virus. Before buying new hardware, always run a full scan and check for unknown executable files. There is more on 10 ways to avoid malware when you browse online in a separate guide.
Safety first: Never end a task from a suspicious file path without first scanning it. Some malware destroys itself or triggers a payload if you kill the process.
When to stop checking and get professional help
You should stop trying to fix this yourself if the system refuses to boot into normal mode, or if Task Manager itself will not open. This indicates a rootkit that has modified the OS kernel. You cannot easily remove these from a compromised environment.
If you find multiple unknown processes, or if clearing one causes others to respawn, the malware has a persistence mechanism. You are fighting a war, not a skirmish. This is the point where a clean reinstall is safer than trying to clean the drive.
If your personal data is on the machine, do not just wipe it. Use a clean, separate computer to back up critical files to an external drive. Do not plug the external drive into the infected PC.
Preventing memory-hungry malware in the future
The best way to keep memory usage predictable is to prevent infection. Keep Windows Update active. Most modern malware exploits unpatched system vulnerabilities to gain the access it needs to run in the background.
Avoid downloading software from unofficial mirrors. This is the primary vector for ‘bundle’ malware that includes adware and miners. Stick to the vendor’s official download page.
Monitor your ‘Performance’ tab in Task Manager once a week. If you notice the ‘Memory’ graph has a new, permanent floor that is 500MB higher than it was last month, investigate immediately. Do not wait for the PC to crash.
The bottom line
Most malware uses less than 100MB, but miners can exceed 1GB. If you see an unknown process using over 200MB, check its file path in Task Manager. If the path is in Temp or Downloads, scan immediately. If your system struggles with basic tasks, consider a memory upgrade to give the OS room to run security tools.
- PCB color may vary (black or green) depending on production batch. Quality and
- DDR3L / DDR3 1600MHz PC3L-12800 / PC3-12800 240-Pin Unbuffered Non-ECC 1.35V / 1.5V
Frequently asked questions
Is it normal for antivirus to use a lot of memory?
Yes. Real-time protection scans files as they load. This can temporarily spike memory by 200-400MB. It should return to baseline (50-100MB) once the scan is complete. If it stays high, the antivirus may be stuck or there is heavy background activity.
My RAM is full, but no single app is using much. Why?
This is usually ‘fragmentation’ or many small background services. Check the ‘Processes’ tab and sum up the memory for all system processes. If total is near your limit, you need more RAM or should disable startup items you do not use.
Can malware hide its memory usage from Task Manager?
Advanced rootkits can hook into the OS to report false values. If you suspect this, use a bootable USB antivirus scanner. This runs outside the Windows environment and cannot be easily fooled by malware running inside the OS.
What is a safe memory usage threshold for gaming?
Gaming PCs usually have 16GB or 32GB. Idle usage should be under 5GB. If idle is above 6GB, something is wrong. If you have 8GB, you do not have enough for modern games, and malware will crush performance instantly.